DATA AND APPLICATION SECURITY
Protect confidential data and corporate applications through data loss prevention, classification, encryption, web application and API security, and code security testing.
DATA AND APPLICATION SECURITY
Protect confidential data and corporate applications through data loss prevention, classification, encryption, web application and API security, and code security testing.
Key benefits
Data and application protection combines information classification, data loss prevention, encryption, cloud environment controls, and development security testing. This approach supports compliance, reduces the risk of data compromise, and protects public services without slowing down the business.
Application security based on recognized methods
Testing follows OWASP Top 10:2025 and OWASP ASVS 5.0.
Data compliance
Controls follow ISO/IEC 27001:2022 and, for payment environments, PCI DSS v4.x requirements.
Classify first, then control
We identify where critical data is stored before configuring policies.
Data loss prevention across all channels
Email, web, cloud services, removable media, and file sharing.
Security that keeps development moving
Application testing is integrated into the delivery cycle without blocking releases.
Cloud workload protection
Policies cover cloud services and container environments as well as on-premises systems.
Key benefits
Data and application protection combines information classification, data loss prevention, encryption, cloud environment controls, and development security testing. This approach supports compliance, reduces the risk of data compromise, and protects public services without slowing down the business.
Application security based on recognized methods
Testing follows OWASP Top 10:2025 and OWASP ASVS 5.0.
Data compliance
Controls follow ISO/IEC 27001:2022 and, for payment environments, PCI DSS v4.x requirements.
Classify first, then control
We identify where critical data is stored before configuring policies.
Data loss prevention across all channels
Email, web, cloud services, removable media, and file sharing.
Security that keeps development moving
Application testing is integrated into the delivery cycle without blocking releases.
Cloud workload protection
Policies cover cloud services and container environments as well as on-premises systems.
Key data and application security capabilities
We begin with discovery: where critical data resides and which applications are externally accessible. The findings determine the security tools and testing schedule.
- Data loss prevention (DLP): Control the transfer of sensitive information outside the company.
- Data classification and data security posture management (DSPM): Discover sensitive data and assess storage risks.
- Web application and API protection (WAF): Filter attacks on public services and interfaces.
- Application security testing: Code analysis, dynamic testing, and API vulnerability assessments.
- Device encryption and data protection: Full-disk encryption and protection for email and file services.
Key data and application security capabilities
We begin with discovery: where critical data resides and which applications are externally accessible. The findings determine the security tools and testing schedule.
- Data loss prevention (DLP): Control the transfer of sensitive information outside the company.
- Data classification and data security posture management (DSPM): Discover sensitive data and assess storage risks.
- Web application and API protection (WAF): Filter attacks on public services and interfaces.
- Application security testing: Code analysis, dynamic testing, and API vulnerability assessments.
- Device encryption and data protection: Full-disk encryption and protection for email and file services.
Data under control at every stage
Protection starts with understanding where sensitive data resides, how it moves, and who can access it.
- Data repository inventory: We identify databases, file shares, cloud services, and devices that store corporate information.
- Data flows: We analyze information moving between employees, applications, branches, cloud platforms, and external recipients.
- Classification and access: We classify data by criticality and define rules for viewing, editing, storing, and transferring it.
- Monitoring and training: We monitor policy violations and train employees to handle sensitive information securely.
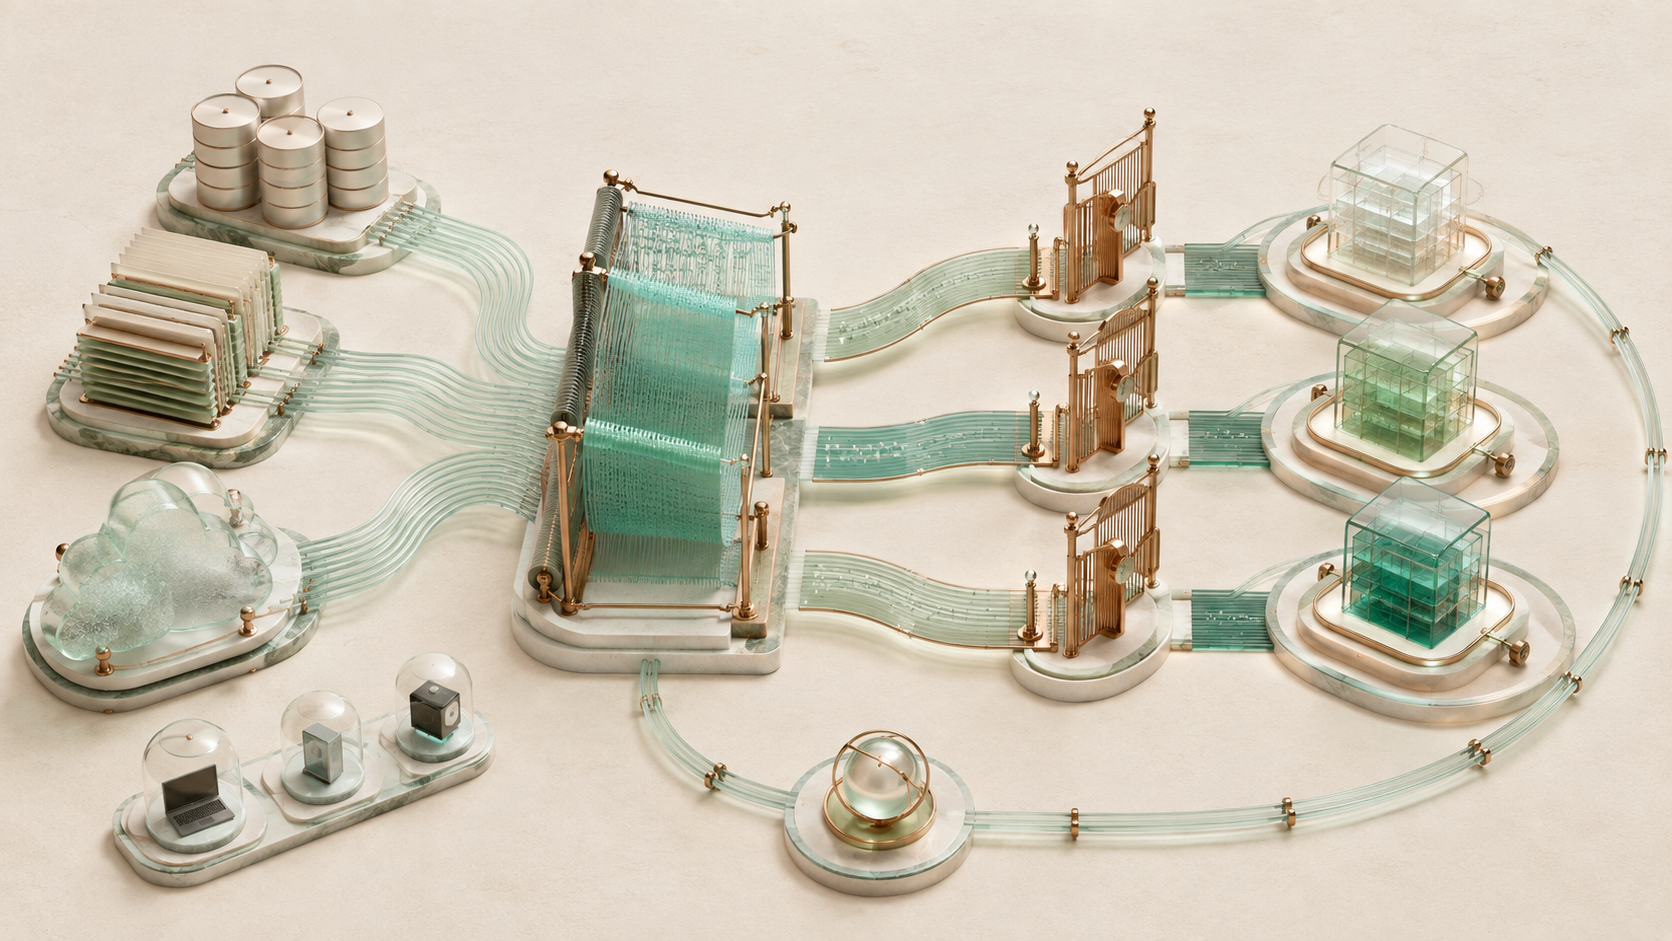
Data under control at every stage
Protection starts with understanding where sensitive data resides, how it moves, and who can access it.
- Data repository inventory: We identify databases, file shares, cloud services, and devices that store corporate information.
- Data flows: We analyze information moving between employees, applications, branches, cloud platforms, and external recipients.
- Classification and access: We classify data by criticality and define rules for viewing, editing, storing, and transferring it.
- Monitoring and training: We monitor policy violations and train employees to handle sensitive information securely.
Applications without weak points
Application security is a continuous process, from testing public services and APIs to fixing vulnerabilities and blocking attacks in real time.
- Public services and APIs: We identify externally accessible applications, interfaces, and connections to corporate systems.
- Vulnerability discovery: We test code, web applications, and APIs for flaws that could compromise data or services.
- Remediation and retesting: We share findings with developers, support remediation, and verify the results through retesting.
- Real-time protection: We configure WAF to filter malicious requests and block attacks on public applications and APIs.
Applications without weak points
Application security is a continuous process, from testing public services and APIs to fixing vulnerabilities and blocking attacks in real time.
- Public services and APIs: We identify externally accessible applications, interfaces, and connections to corporate systems.
- Vulnerability discovery: We test code, web applications, and APIs for flaws that could compromise data or services.
- Remediation and retesting: We share findings with developers, support remediation, and verify the results through retesting.
- Real-time protection: We configure WAF to filter malicious requests and block attacks on public applications and APIs.
The value of partnership
We cover the organizational and technical aspects, from data handling policies to security tool deployment and regular application testing.
The value of partnership
We cover the organizational and technical aspects, from data handling policies to security tool deployment and regular application testing.
Related services
Related capabilities strengthen data and application protection: access management restricts access to critical information, backups enable recovery, and vulnerability management reduces the risk of exploitation.
Identity and access management
We centralize user and permission management and implement MFA and role-based access to reduce unauthorized access risks and update or revoke rights promptly.
Backup and disaster recovery
We protect data and critical services with immutable backups and tested recovery procedures with defined RPO and RTO targets.
Vulnerability management
We regularly identify infrastructure and application weaknesses, assess severity, and prioritize remediation. This reduces incident likelihood and keeps IT security at a controlled level.
Want to learn more about this service?
We identify where your confidential data is least protected.
Related services
Related capabilities strengthen data and application protection: access management restricts access to critical information, backups enable recovery, and vulnerability management reduces the risk of exploitation.
Identity and access management
We centralize user and permission management and implement MFA and role-based access to reduce unauthorized access risks and update or revoke rights promptly.
Backup and disaster recovery
We protect data and critical services with immutable backups and tested recovery procedures with defined RPO and RTO targets.
Vulnerability management
We regularly identify infrastructure and application weaknesses, assess severity, and prioritize remediation. This reduces incident likelihood and keeps IT security at a controlled level.
Want to learn more about this service?
We identify where your confidential data is least protected.