THREAT MANAGEMENT AND RESPONSE
(Threat Management & Response)
Detect attacks and coordinate incident response with endpoint protection, security event collection and correlation, threat intelligence, and managed monitoring services.
THREAT MANAGEMENT & RESPONSE
Detect attacks and coordinate incident response with endpoint protection, security event collection and correlation, threat intelligence, and managed monitoring services.
Key benefits
A unified threat management framework combines endpoint protection, event collection and correlation, attack analytics, and structured response. It provides visibility across the infrastructure, helps separate critical incidents from noise faster, and keeps the team prepared, whether working independently or with a managed SOC.
Standards-based response
Processes follow NIST CSF 2.0 and ISO/IEC 27035-1:2023 for information security incident management.
Understanding attacker tactics
Detection use cases are mapped to MITRE ATT&CK, extending beyond signature-based detection.
Full infrastructure visibility
Events from endpoints, servers, networks, email, and cloud services are brought together into a unified view.
Speed without overload
Correlation and prioritization reduce false positives and free up IT resources.
An option without an in-house SOC
Managed detection and response services are available for organizations without a dedicated security team.
Readiness checks
Response drills and incident reviews with policy updates.
Key benefits
A unified threat management framework combines endpoint protection, event collection and correlation, attack analytics, and structured response. It provides visibility across the infrastructure, helps separate critical incidents from noise faster, and keeps the team prepared, whether working independently or with a managed SOC.
Standards-based response
Processes follow NIST CSF 2.0 and ISO/IEC 27035-1:2023 for information security incident management.
Understanding attacker tactics
Detection use cases are mapped to MITRE ATT&CK, extending beyond signature-based detection.
Full infrastructure visibility
Events from endpoints, servers, networks, email, and cloud services are brought together into a unified view.
Speed without overload
Correlation and prioritization reduce false positives and free up IT resources.
An option without an in-house SOC
Managed detection and response services are available for organizations without a dedicated security team.
Readiness checks
Response drills and incident reviews with policy updates.
Unified detection and response
Detection is introduced in stages: endpoint protection and basic event collection first, followed by correlation, threat analytics, and, if needed, external round-the-clock monitoring.
- Endpoint protection (EPP and EDR): Prevent, detect, and investigate attacks on workstations and servers.
- Extended detection and response (XDR): Connect events from different security layers into one incident.
- SIEM and security event management: Centralized log collection, correlation, and storage.
- Managed detection and response (MDR): Round-the-clock external monitoring through vendor-managed services.
- Threat intelligence and dark web monitoring: Information on threats, leaked credentials, and company mentions.
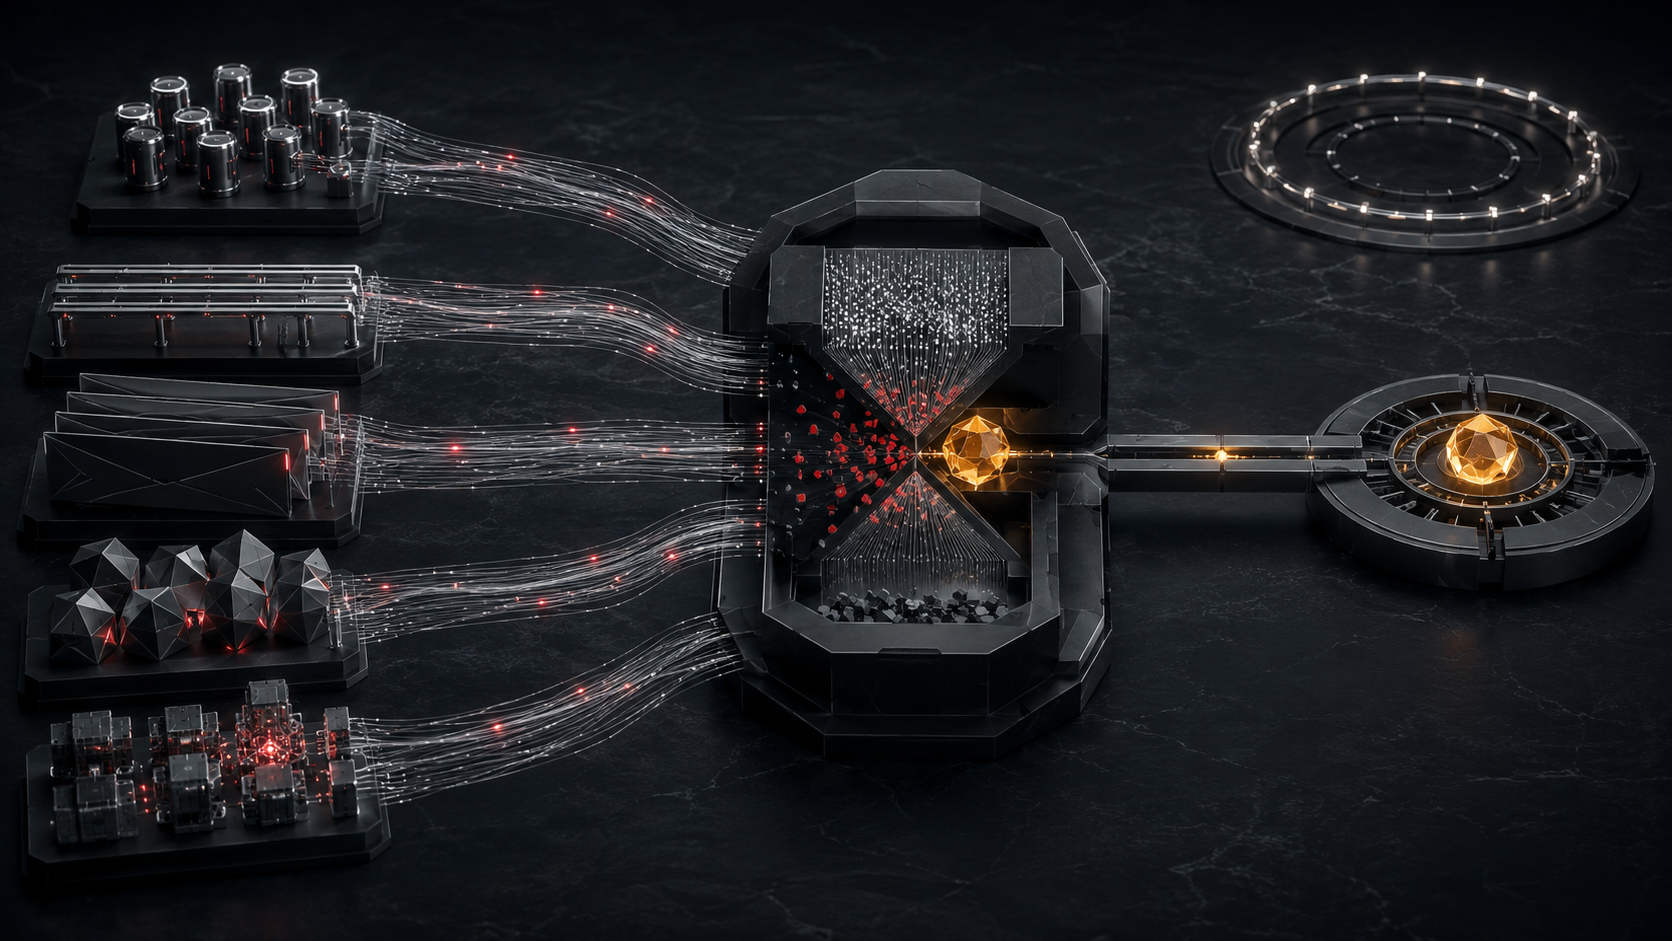
Unified detection and response
Detection is introduced in stages: endpoint protection and basic event collection first, followed by correlation, threat analytics, and, if needed, external round-the-clock monitoring.
- Endpoint protection (EPP and EDR): Prevent, detect, and investigate attacks on workstations and servers.
- Extended detection and response (XDR): Connect events from different security layers into one incident.
- SIEM and security event management: Centralized log collection, correlation, and storage.
- Managed detection and response (MDR): Round-the-clock external monitoring through vendor-managed services.
- Threat intelligence and dark web monitoring: Information on threats, leaked credentials, and company mentions.
Detection tailored to your infrastructure
We design detection around critical assets, realistic attack scenarios, and the specifics of your infrastructure.
- Critical assets: we identify systems, data, and services whose disruption poses the greatest business risk.
- Attack scenarios: we map likely attack paths and control points for early detection.
- Event sources: we connect endpoints, servers, networks, email, cloud platforms, and security tools.
- Rules and priorities: we configure event correlation and on-duty team procedures for different threat types.
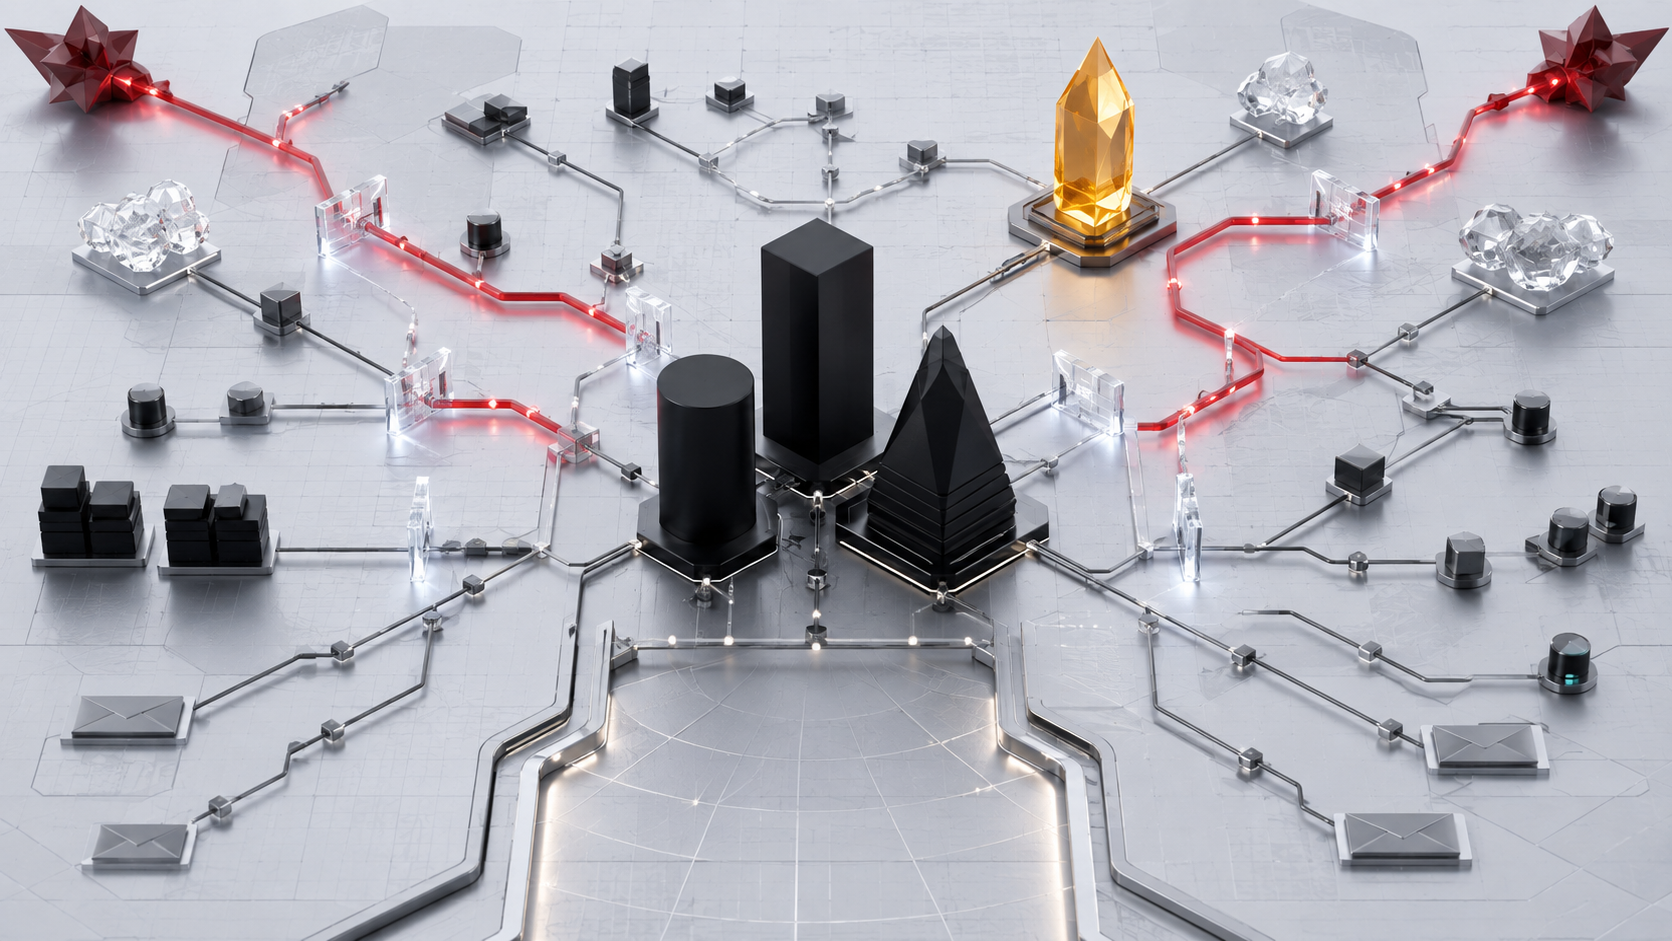
Detection tailored to your infrastructure
We design detection around critical assets, realistic attack scenarios, and the specifics of your infrastructure.
- Critical assets: we identify systems, data, and services whose disruption poses the greatest business risk.
- Attack scenarios: we map likely attack paths and control points for early detection.
- Event sources: we connect endpoints, servers, networks, email, cloud platforms, and security tools.
- Rules and priorities: we configure event correlation and on-duty team procedures for different threat types.
Clear incident response procedures
Every incident follows a predefined playbook, from initial assessment through service recovery and improvements to security policies.
- Classification: we determine the incident type, scale, criticality, and potential business impact.
- Escalation: we assign responsible specialists and involve the required management levels.
- Containment and recovery: we isolate affected systems, remediate the impact, and restore services.
- Incident review: we document causes and lessons learned, then refine detection rules, procedures, and security policies.
Clear incident response procedures
Every incident follows a predefined playbook, from initial assessment through service recovery and improvements to security policies.
- Classification: we determine the incident type, scale, criticality, and potential business impact.
- Escalation: we assign responsible specialists and involve the required management levels.
- Containment and recovery: we isolate affected systems, remediate the impact, and restore services.
- Incident review: we document causes and lessons learned, then refine detection rules, procedures, and security policies.
Technology, processes, and support in one environment
We combine technology from multiple vendors with procedures, roles, training, and support to build an effective security operation that goes beyond a collection of installed products.
Technology, processes, and support in one environment
We combine technology from multiple vendors with procedures, roles, training, and support to build an effective security operation that goes beyond a collection of installed products.
Related services
Effective detection and response require a comprehensive approach: vulnerability management reduces the attack surface, network security limits threat propagation, and data and application protection reduce incident impact. Together, they create a unified framework for prevention, detection, and response.
Vulnerability management
We regularly identify infrastructure and application weaknesses, assess severity, and prioritize remediation. This reduces incident likelihood and keeps IT security at a controlled level.
Network security
We secure wired and wireless connections, control user and device access, segment networks, and prevent threats from spreading between corporate systems.
DATA AND APPLICATION SECURITY
We protect corporate data, applications, databases, and cloud services against leaks, corruption, and unauthorized access throughout the infrastructure.
Want to learn more about this service?
We assess threat visibility across your infrastructure
Related services
Effective detection and response require a comprehensive approach: vulnerability management reduces the attack surface, network security limits threat propagation, and data and application protection reduce incident impact. Together, they create a unified framework for prevention, detection, and response.
Vulnerability management
We regularly identify infrastructure and application weaknesses, assess severity, and prioritize remediation. This reduces incident likelihood and keeps IT security at a controlled level.
Network security
We secure wired and wireless connections, control user and device access, segment networks, and prevent threats from spreading between corporate systems.
DATA AND APPLICATION SECURITY
We protect corporate data, applications, databases, and cloud services against leaks, corruption, and unauthorized access throughout the infrastructure.
Want to learn more about this service?
We assess threat visibility across your infrastructure