IDENTITY AND ACCESS MANAGEMENT
Control who can access what with multifactor authentication, privileged account management, single sign-on, and Zero Trust access principles.
IDENTITY AND ACCESS MANAGEMENT
Control who can access what with multifactor authentication, privileged account management, single sign-on, and Zero Trust access principles.
Key benefits
Identity and access management combines identity verification, privilege control, and ongoing permission management. Every request is verified under Zero Trust principles, while MFA, passwordless sign-in, and single sign-on improve security and simplify employees' work.
Identity verification aligned with current requirements
Solutions are designed in line with NIST SP 800-63-4 (Digital Identity Guidelines, 2025).
Zero Trust architecture
Access is granted by verifying every request in accordance with NIST SP 800-207, rather than trusting a device's presence inside the network.
Privilege control
Administrative accounts are brought under control: access is granted on request, and sessions are logged.
Protection against compromised passwords
Multifactor and passwordless authentication address the most common attack vector.
Organized access permissions
Access reviews and revocations become a regular ISO/IEC 27001:2022 procedure rather than a one-time exercise.
Employee convenience
Single sign-on reduces the number of passwords and support requests.
Key benefits
Identity and access management combines identity verification, privilege control, and ongoing permission management. Every request is verified under Zero Trust principles, while MFA, passwordless sign-in, and single sign-on improve security and simplify employees' work.
Identity verification aligned with current requirements
Solutions are designed in line with NIST SP 800-63-4 (Digital Identity Guidelines, 2025).
Zero Trust architecture
Access is granted by verifying every request in accordance with NIST SP 800-207, rather than trusting a device's presence inside the network.
Privilege control
Administrative accounts are brought under control: access is granted on request, and sessions are logged.
Protection against compromised passwords
Multifactor and passwordless authentication address the most common attack vector.
Organized access permissions
Access reviews and revocations become a regular ISO/IEC 27001:2022 procedure rather than a one-time exercise.
Employee convenience
Single sign-on reduces the number of passwords and support requests.
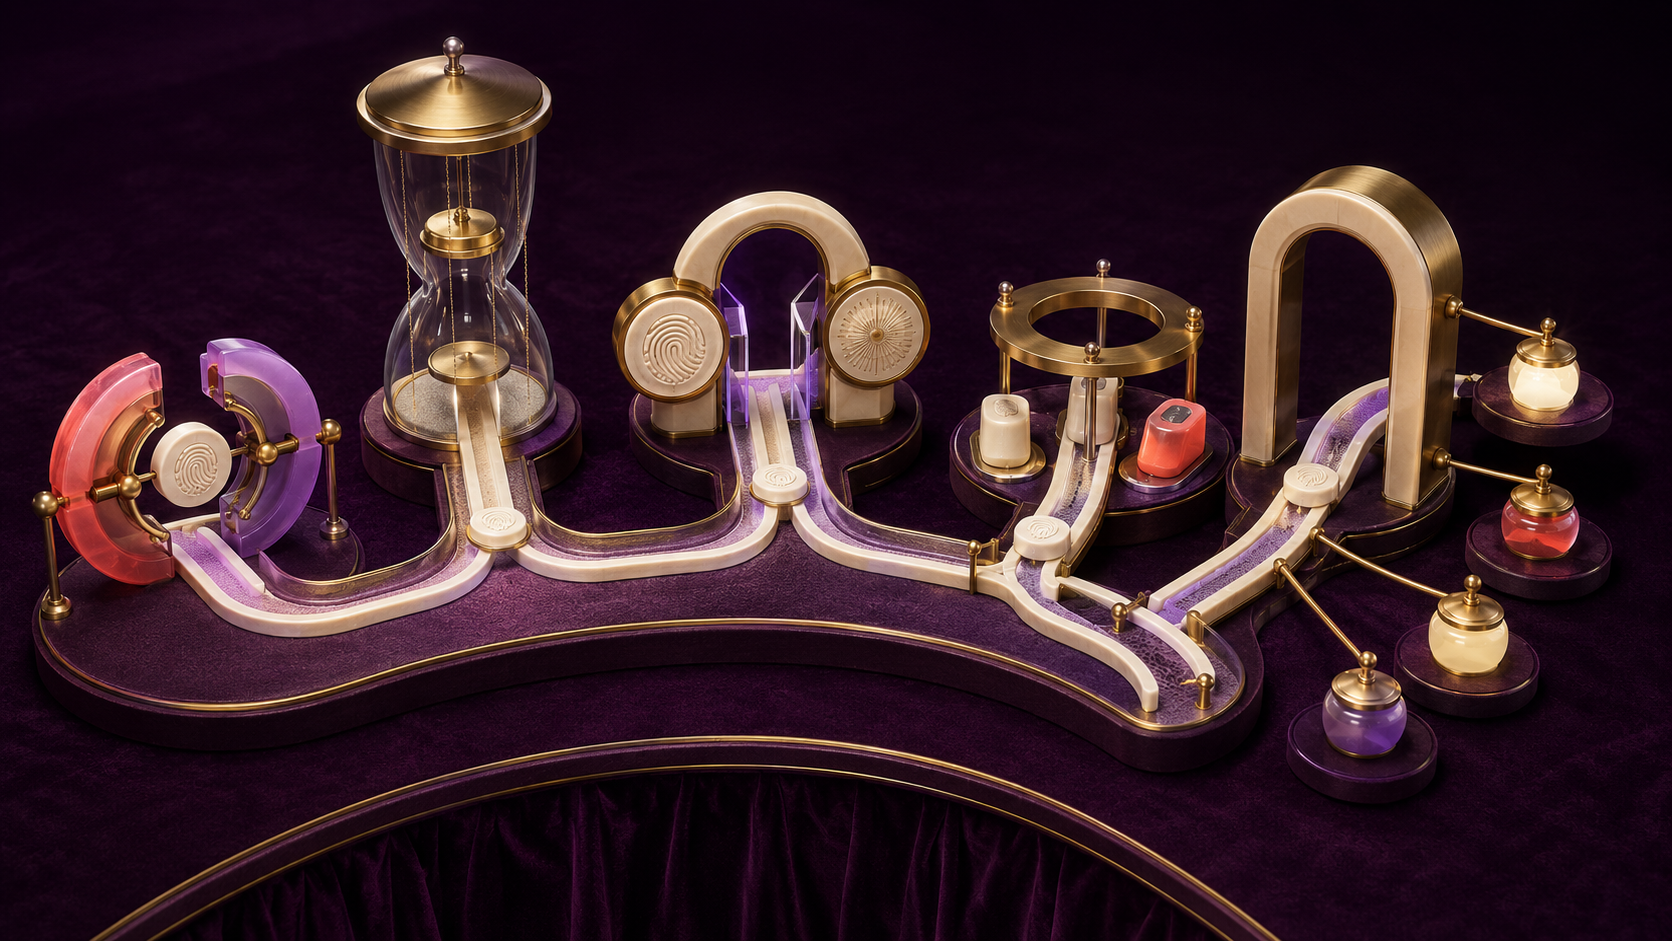
Key access management capabilities
Implementation usually starts with multifactor authentication for critical systems and remote access, followed by privileged access management, single sign-on, and device access controls.
- Multifactor authentication (MFA): A second authentication factor for critical systems and remote access.
- Privileged access management (PAM): Secure administrative credential storage, on-demand access, and session recording.
- Passwordless authentication: Sign in with certificates and devices instead of passwords.
- Network device access management (NAC, RADIUS, TACACS+): Verify device policy compliance before granting access.
- Single sign-on and Zero Trust Access: Centralized authentication and application access without exposing the entire network.
Key access management capabilities
Implementation usually starts with multifactor authentication for critical systems and remote access, followed by privileged access management, single sign-on, and device access controls.
- Multifactor authentication (MFA): A second authentication factor for critical systems and remote access.
- Privileged access management (PAM): Secure administrative credential storage, on-demand access, and session recording.
- Passwordless authentication: Sign in with certificates and devices instead of passwords.
- Network device access management (NAC, RADIUS, TACACS+): Verify device policy compliance before granting access.
- Single sign-on and Zero Trust Access: Centralized authentication and application access without exposing the entire network.
Identity management in order
Access management starts with a complete view of accounts, assigned permissions, and users' connections to corporate systems.
- Inventory: we gather information on employees, service accounts, external users, and their assigned permissions.
- Account cleanup: We identify unused, duplicate, and excessive accounts that create additional risk.
- Role model: We group permissions into clear business roles based on job positions, functions, and least privilege.
- Access reviews: we establish regular access confirmation and revocation with the responsible system owners.
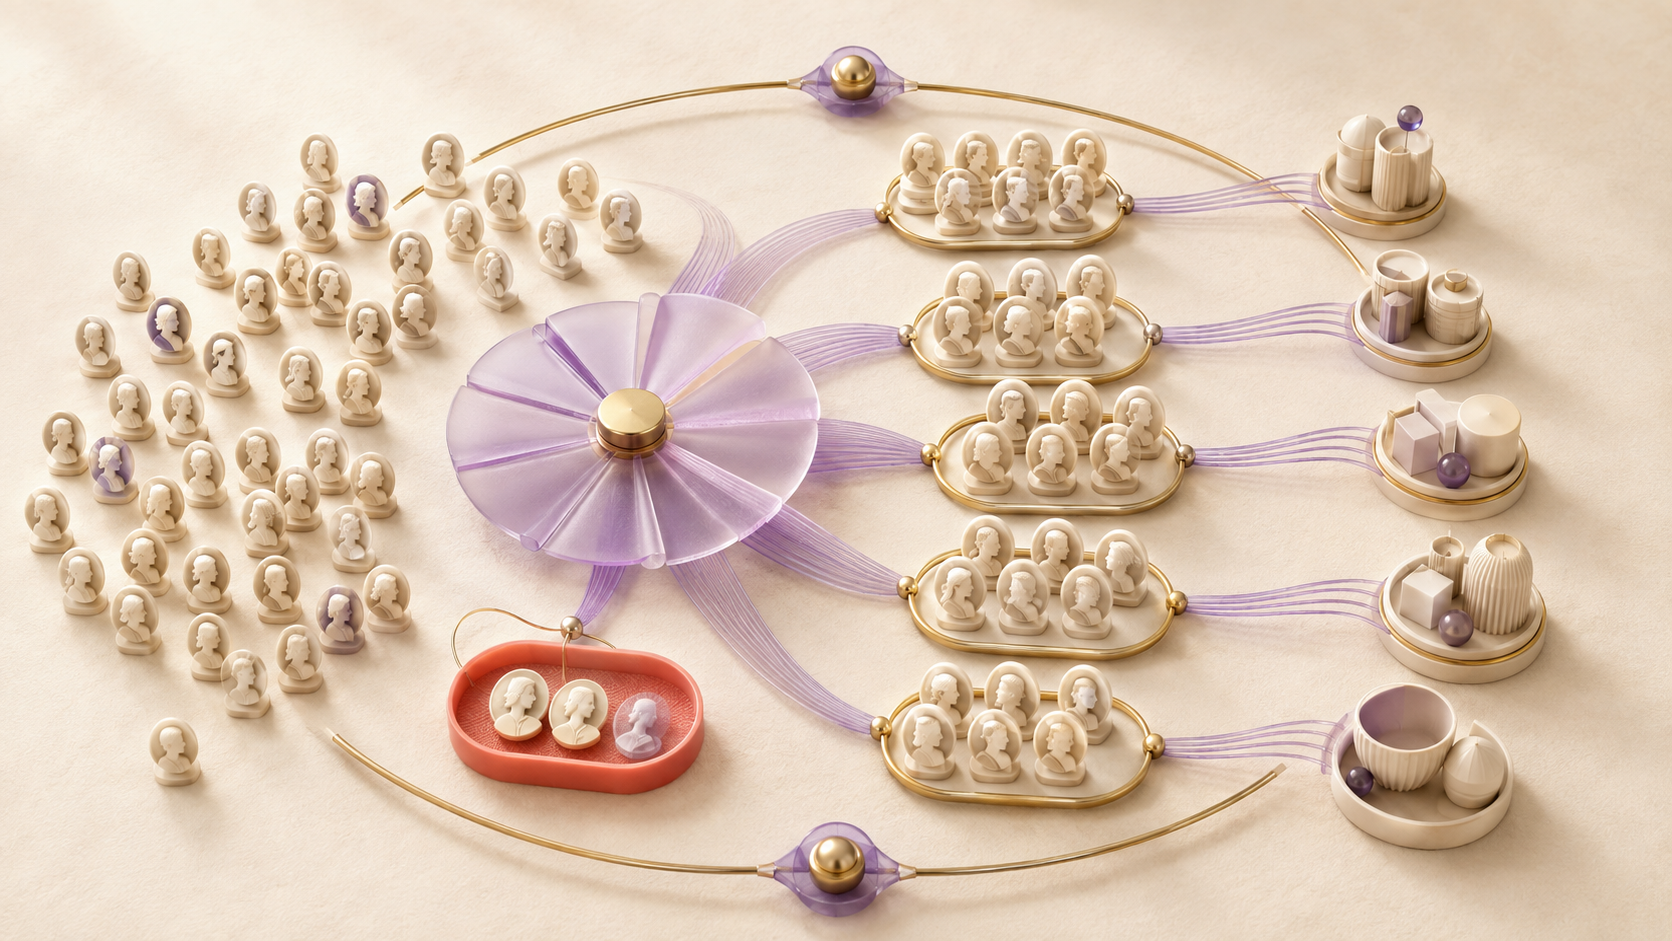
Identity management in order
Access management starts with a complete view of accounts, assigned permissions, and users' connections to corporate systems.
- Inventory: we gather information on employees, service accounts, external users, and their assigned permissions.
- Account cleanup: We identify unused, duplicate, and excessive accounts that create additional risk.
- Role model: We group permissions into clear business roles based on job positions, functions, and least privilege.
- Access reviews: we establish regular access confirmation and revocation with the responsible system owners.
Privileged access under control
Administrative privileges are granted only after verification, for a limited time, and with full monitoring of user actions.
- Credential isolation: Administrative passwords and keys are stored in a secure PAM vault and are not shared directly with users.
- Temporary access: Elevated privileges are granted on request for a specific task and automatically revoked when the approved period expires.
- Session recording: Administrator actions are recorded, with recordings used for incident investigation and compliance reviews.
- External contractors: Third-party specialists follow a separate policy with stronger verification, restricted access, and mandatory session monitoring.
Privileged access under control
Administrative privileges are granted only after verification, for a limited time, and with full monitoring of user actions.
- Credential isolation: Administrative passwords and keys are stored in a secure PAM vault and are not shared directly with users.
- Temporary access: Elevated privileges are granted on request for a specific task and automatically revoked when the approved period expires.
- Session recording: Administrator actions are recorded, with recordings used for incident investigation and compliance reviews.
- External contractors: Third-party specialists follow a separate policy with stronger verification, restricted access, and mandatory session monitoring.
The value of partnership
We implement both the technical and organizational elements: a role model, access provisioning and revocation procedures, MFA and PAM deployment, directory and business application integration, and administrator training.
The value of partnership
We implement both the technical and organizational elements: a role model, access provisioning and revocation procedures, MFA and PAM deployment, directory and business application integration, and administrator training.
Related services
Access management is complemented by network security, data protection, and accurate IT asset tracking. Together, they help verify users and devices, restrict access to critical resources, and update or revoke permissions promptly.
Network security
We secure wired and wireless connections, control user and device access, segment networks, and prevent threats from spreading between corporate systems.
DATA AND APPLICATION SECURITY
We protect corporate data, applications, databases, and cloud services against leaks, corruption, and unauthorized access throughout the infrastructure.
IT ASSET MANAGEMENT
We create a unified inventory of hardware, software, and licenses throughout their lifecycle, from purchasing and commissioning to maintenance and retirement.
Want to learn more about this service?
We audit accounts and access rights to show the actual state of access.
Related services
Access management is complemented by network security, data protection, and accurate IT asset tracking. Together, they help verify users and devices, restrict access to critical resources, and update or revoke permissions promptly.
Network security
We secure wired and wireless connections, control user and device access, segment networks, and prevent threats from spreading between corporate systems.
DATA AND APPLICATION SECURITY
We protect corporate data, applications, databases, and cloud services against leaks, corruption, and unauthorized access throughout the infrastructure.
IT ASSET MANAGEMENT
We create a unified inventory of hardware, software, and licenses throughout their lifecycle, from purchasing and commissioning to maintenance and retirement.
Want to learn more about this service?
We audit accounts and access rights to show the actual state of access.