VULNERABILITY MANAGEMENT
Continuously identify, prioritize, and remediate infrastructure and application vulnerabilities, with measurable risk reduction.
VULNERABILITY MANAGEMENT
Continuously identify, prioritize, and remediate infrastructure and application vulnerabilities, with measurable risk reduction.
Key benefits
We systematically identify vulnerabilities, prioritize them by actual risk, and track remediation through to a verified result.
Risk-based prioritization
Vulnerability assessment is based on CVSS v4.0 and actual asset criticality, going beyond a long list of generic findings.
Processes based on recognized guidance
Patch management follows NIST SP 800-40 Rev. 4, with the overall framework based on NIST CSF 2.0 and CIS Controls v8.1.
External attack surface visibility
Discover forgotten services, subdomains, and exposed interfaces that IT teams may be unaware of.
From scanning to remediation
We see remediation through to closure and verify the result, going beyond a vulnerability report.
Verifying real-world exploitability
Penetration testing shows which vulnerabilities can actually lead to compromise.
A regular process rather than one-off campaigns
Scanning and patching cycles follow documented procedures, with reporting for management.
Key benefits
We systematically identify vulnerabilities, prioritize them by actual risk, and track remediation through to a verified result.
Risk-based prioritization
Vulnerability assessment is based on CVSS v4.0 and actual asset criticality, going beyond a long list of red flags.
Processes based on recognized guidance
Patch management follows NIST SP 800-40 Rev. 4, with the overall framework based on NIST CSF 2.0 and CIS Controls v8.1.
External attack surface visibility
Discover forgotten services, subdomains, and exposed interfaces that IT teams may be unaware of.
From scanning to remediation
We see remediation through to closure and verify the result, going beyond a vulnerability report.
Verifying real-world exploitability
Penetration testing shows which vulnerabilities can actually lead to compromise.
A regular process rather than one-off campaigns
Scanning and patching cycles follow documented procedures, with reporting for management.
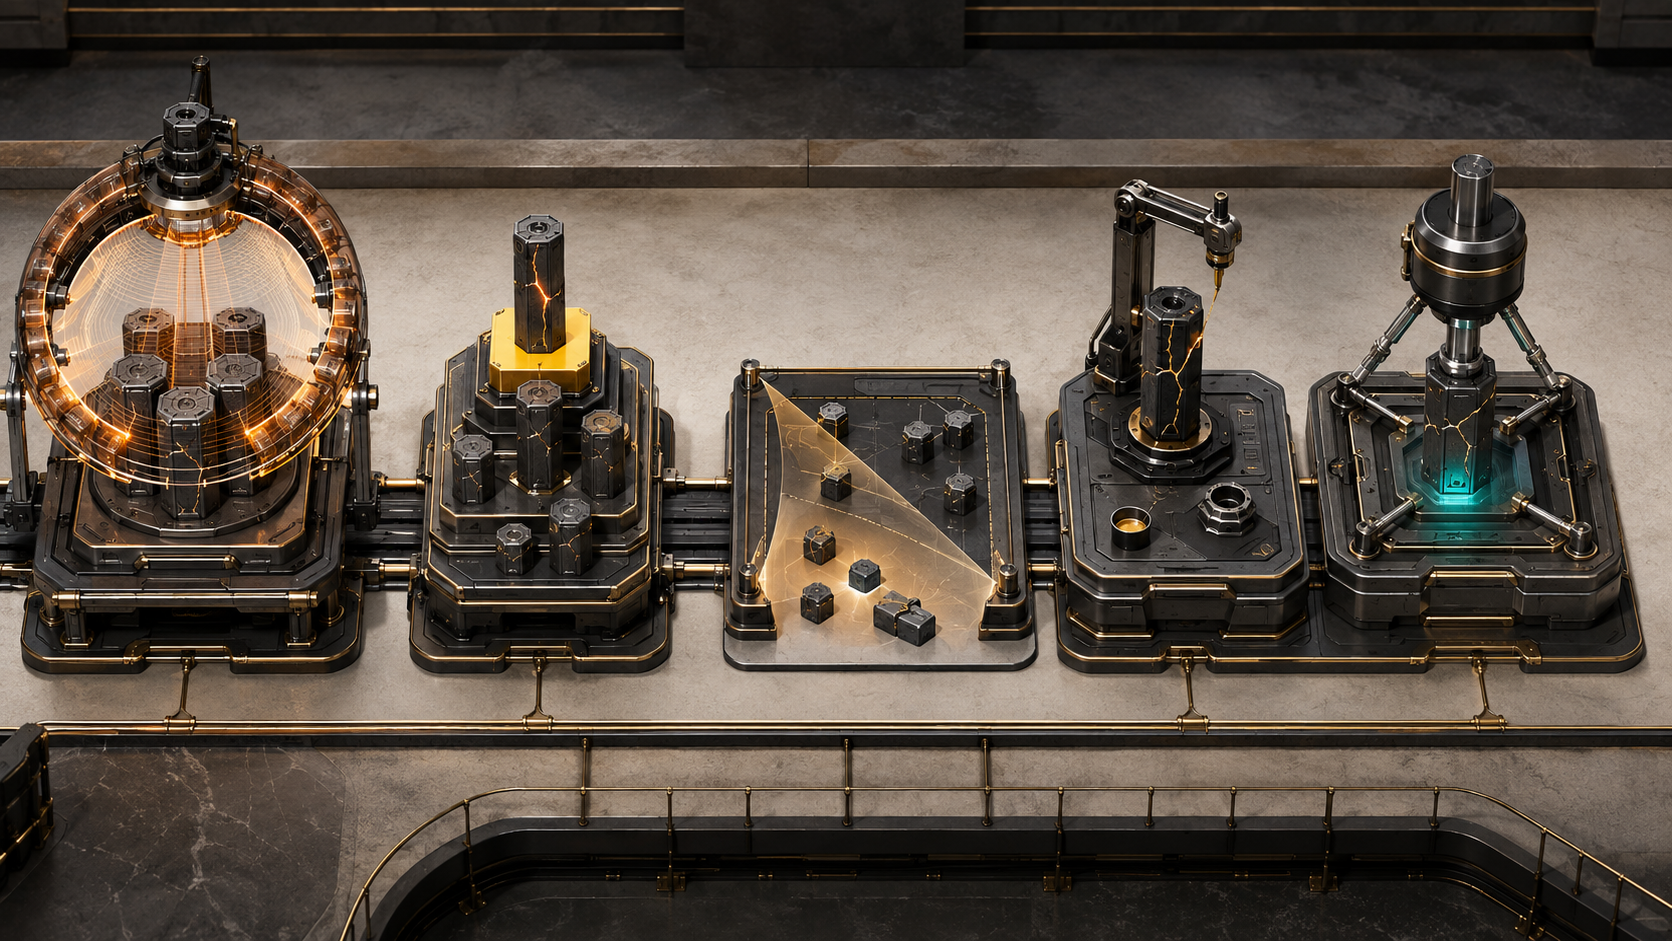
Key vulnerability management capabilities
We agree on the scope with you: the external perimeter, internal infrastructure, endpoints, web applications, and APIs. We then define assessment frequency and update windows.
- Infrastructure and application scanning: Identify vulnerabilities on servers, workstations, network equipment, and web services.
- Risk-based vulnerability management (Risk-Based VM): Prioritization by asset criticality, external exposure, and exploit availability.
- Attack surface management (ASM): Inventory the company's externally accessible resources.
- Patch management: Plan, test, and deploy updates, then verify the results.
- Penetration testing: Test defenses under conditions that closely simulate a real attack.
Key vulnerability management capabilities
We agree on the scope with you: the external perimeter, internal infrastructure, endpoints, web applications, and APIs. We then define assessment frequency and update windows.
- Infrastructure and application scanning: Identify vulnerabilities on servers, workstations, network equipment, and web services.
- Risk-based vulnerability management (Risk-Based VM): Prioritization by asset criticality, external exposure, and exploit availability.
- Attack surface management (ASM): Inventory the company's externally accessible resources.
- Patch management: Plan, test, and deploy updates, then verify the results.
- Penetration testing: Test defenses under conditions that closely simulate a real attack.
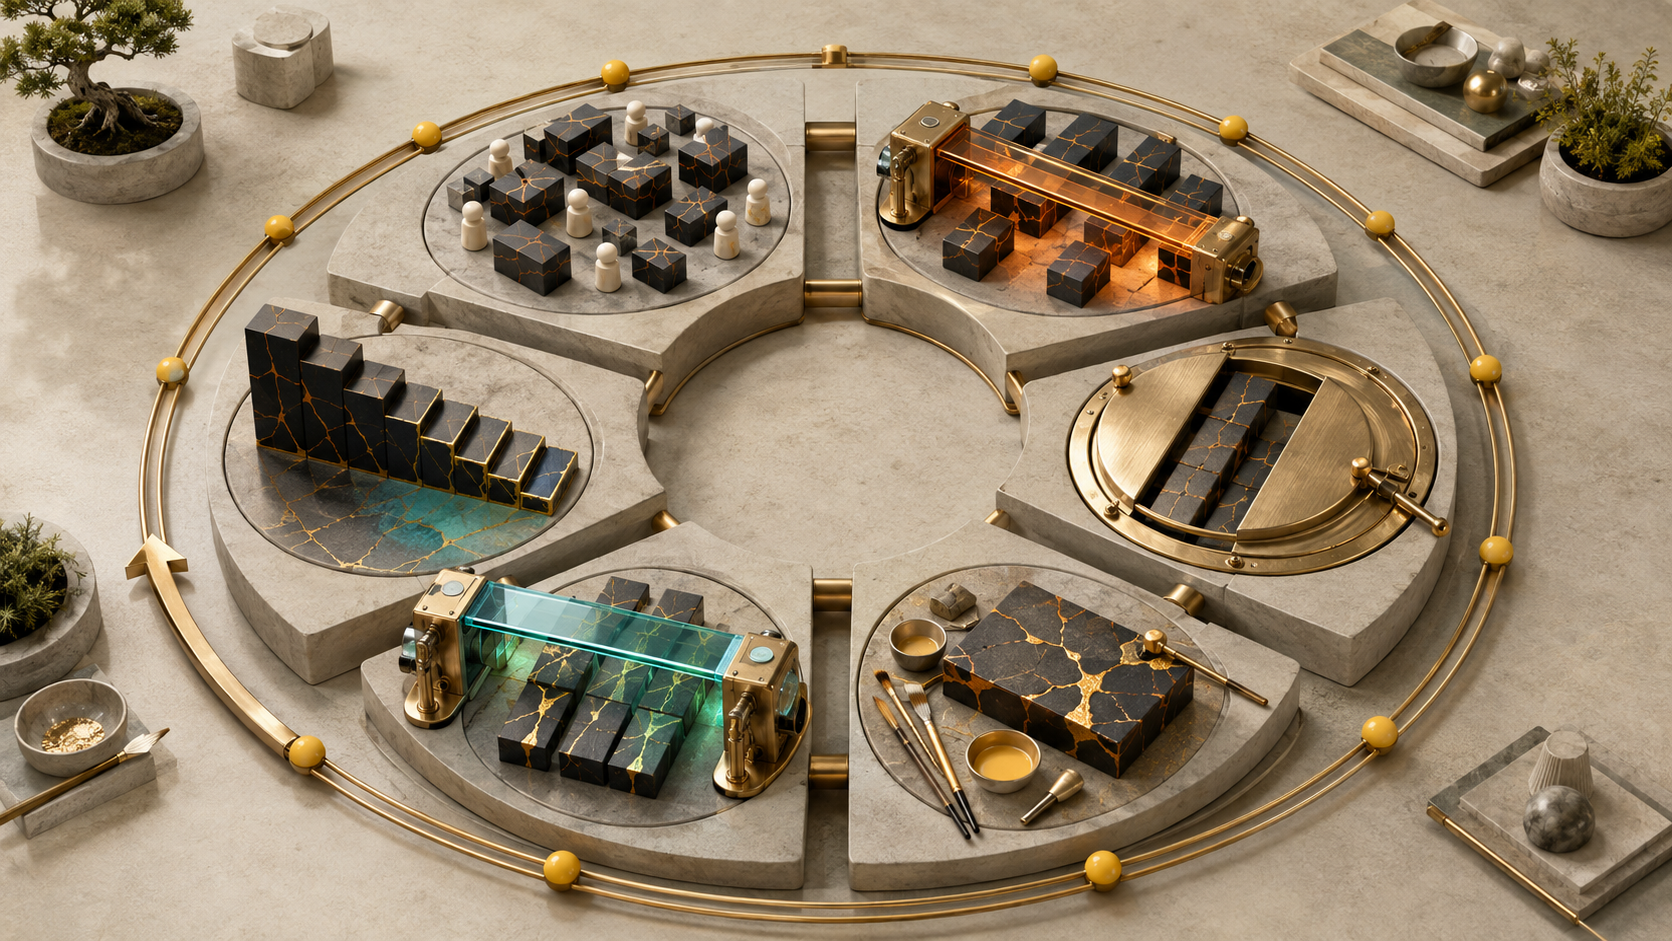
A continuous vulnerability management cycle
Vulnerability management is continuous, from assessment scoping through verified remediation and risk change evaluation.
- Scope and owners: We define the infrastructure, applications, and devices included in scanning and assign an owner to every asset.
- Regular assessments: We set scanning frequency according to system criticality and the pace of infrastructure change.
- Update windows: We agree on testing and patch deployment times that keep business services running.
- Remediation tracking: We track assigned tasks and retest systems after updates are installed.
- Risk trends: We report on open, resolved, and recurring vulnerabilities.
A continuous vulnerability management cycle
Vulnerability management is continuous, from assessment scoping through verified remediation and risk change evaluation.
- Scope and owners: We define the infrastructure, applications, and devices included in scanning and assign an owner to every asset.
- Regular assessments: We set scanning frequency according to system criticality and the pace of infrastructure change.
- Update windows: We agree on testing and patch deployment times that keep business services running.
- Remediation tracking: We track assigned tasks and retest systems after updates are installed.
- Risk trends: We report on open, resolved, and recurring vulnerabilities.
An outside view of your perimeter
We assess infrastructure from an attacker's perspective, identifying internet-accessible resources and security gaps.
- Exposed services: We identify externally accessible servers, ports, admin panels, web applications, and APIs.
- Untracked assets: We find forgotten subdomains, test environments, and services missing from the internal register.
- Outdated software: We identify externally accessible systems with known vulnerabilities and unsupported versions.
- Configuration errors: We review cloud resource settings, network interfaces, and public services.
- Credential leaks: We monitor corporate email addresses, passwords, and other signs of compromise found in public sources.
An outside view of your perimeter
We assess infrastructure from an attacker's perspective, identifying internet-accessible resources and security gaps.
- Exposed services: We identify externally accessible servers, ports, admin panels, web applications, and APIs.
- Untracked assets: We find forgotten subdomains, test environments, and services missing from the internal register.
- Outdated software: We identify externally accessible systems with known vulnerabilities and unsupported versions.
- Configuration errors: We review cloud resource settings, network interfaces, and public services.
- Credential leaks: We monitor corporate email addresses, passwords, and other signs of compromise found in public sources.
The value of partnership
We handle the operational work: configuring scans, reviewing results, agreeing on priorities with your administrators, and tracking remediation, including reports for management and auditors.
The value of partnership
We handle the operational work: configuring scans, reviewing results, agreeing on priorities with your administrators, and tracking remediation, including reports for management and auditors.
Related services
Vulnerability management works best alongside threat detection, data protection, and accurate IT asset tracking. These capabilities complement one another to form a unified security framework.
DATA AND APPLICATION SECURITY.
We protect corporate data, applications, databases, and cloud services against leaks, corruption, and unauthorized access throughout the infrastructure.
Threat management and response
We identify and prioritize threats, contain incidents, and coordinate remediation to reduce response times and limit cyberattack impact.
IT ASSET MANAGEMENT
We create a unified inventory of hardware, software, and licenses throughout their lifecycle, from purchasing and commissioning to maintenance and retirement.
Want to learn more about this service?
We perform a diagnostic scan and identify priority risks
Related services
Vulnerability management works best alongside threat detection, data protection, and accurate IT asset tracking. These capabilities complement one another to form a unified security framework.
DATA AND APPLICATION SECURITY.
We protect corporate data, applications, databases, and cloud services against leaks, corruption, and unauthorized access throughout the infrastructure.
Threat management and response
We identify and prioritize threats, contain incidents, and coordinate remediation to reduce response times and limit cyberattack impact.
IT ASSET MANAGEMENT
We create a unified inventory of hardware, software, and licenses throughout their lifecycle, from purchasing and commissioning to maintenance and retirement.
Want to learn more about this service?
We perform a diagnostic scan and identify priority risks